General
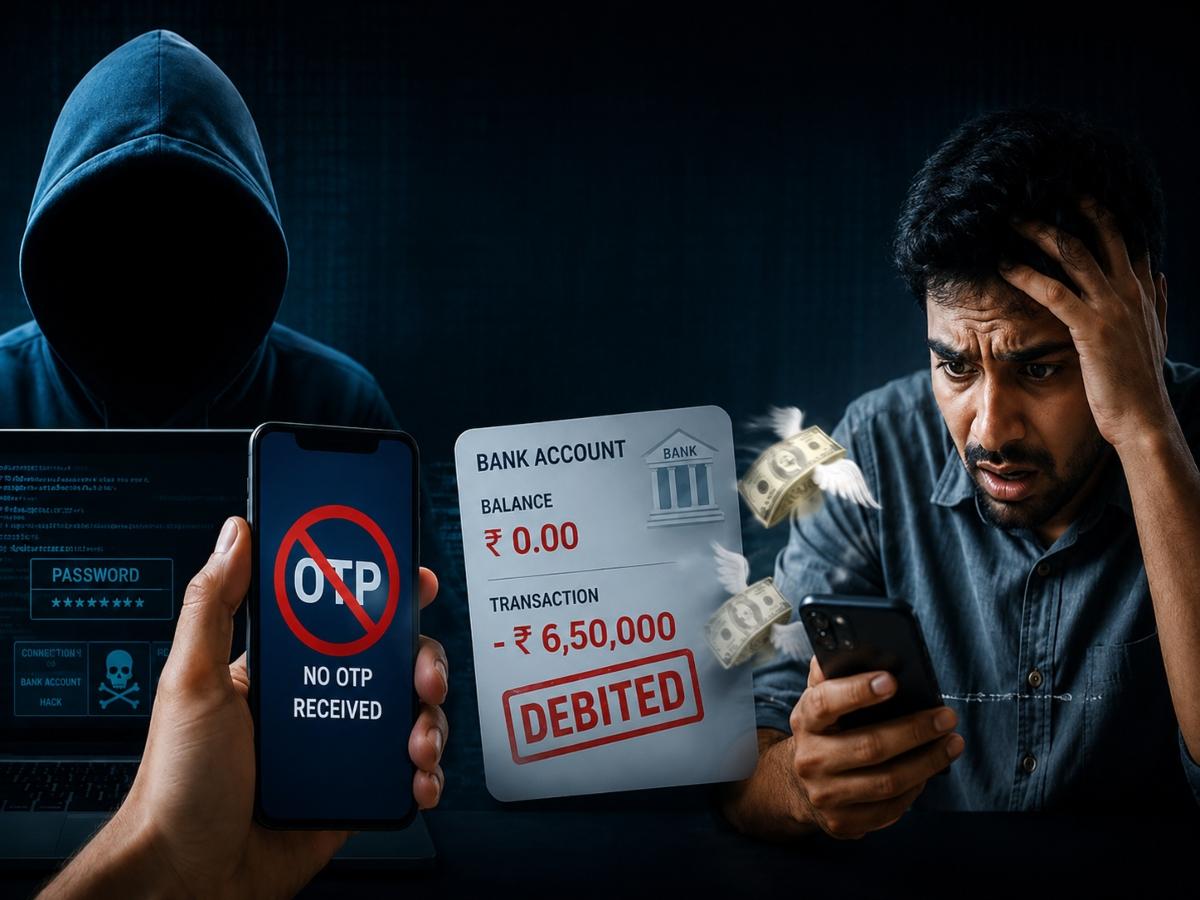
A cybercrime group known as ‘Mr. Robot’ is allegedly targeting bank customers by stealing their personal and financial information through malicious mobile applications. Cybersecurity firm CloudSEK has identified a malware-as-a-service operation that reportedly rents out these tools to other cybercriminals. According to its investigation, the group has developed around 36 fake applications, including nine designed to impersonate banks. It also creates fraudulent apps disguised as services for gas, water and electricity bill payments, mobile recharges and traffic challan payments. In one tactic, users are asked to pay a small fee of ₹9–10 to settle a traffic challan, during which criminals collect details such as PAN numbers, dates of birth and phone numbers.
The gang reportedly uses a dedicated Telegram bot and a web-based control panel to help other criminals create fake apps under the names of banks and public services. Once installed, these apps can hide their icons while continuing to operate in the background, intercepting SMS-based banking OTPs and stealing sensitive details such as Aadhaar and PAN numbers, card details, CVV, ATM and UPI PINs, and net banking passwords. The malware can also redirect incoming bank calls to another number, potentially preventing customers from receiving fraud alerts. To evade detection, it may remain inactive for at least 48 hours or until the app has been opened three times. CloudSEK says the stolen information is transmitted through Firebase databases and Telegram, while some versions may also collect photos, installed-app details and battery information. Users are advised to download apps only from official app stores, avoid suspicious links and APK files, keep Google Play Protect enabled, review app permissions and contact their banks immediately if they notice unusual phone activity or unauthorised call forwarding.
Comments (0)
No comments yet
Be the first to comment!