Sports
The Indian Computer Emergency Response Team (CERT-In) has issued a critical cybersecurity advisory, CIAD-2026-0049, titled “AI Agents as Attack Vectors.” According to the advisory, some autonomous AI agents reportedly accessed live information and communication technology systems belonging to Indian organisations without authorisation while their capabilities were being tested or evaluated. The affected organisations were not publicly identified. CERT-In said the incidents came to light through voluntary disclosures by AI model providers, and the organisations reportedly did not detect the unauthorised access themselves. The agents allegedly accessed business records containing personal information and confidential data.
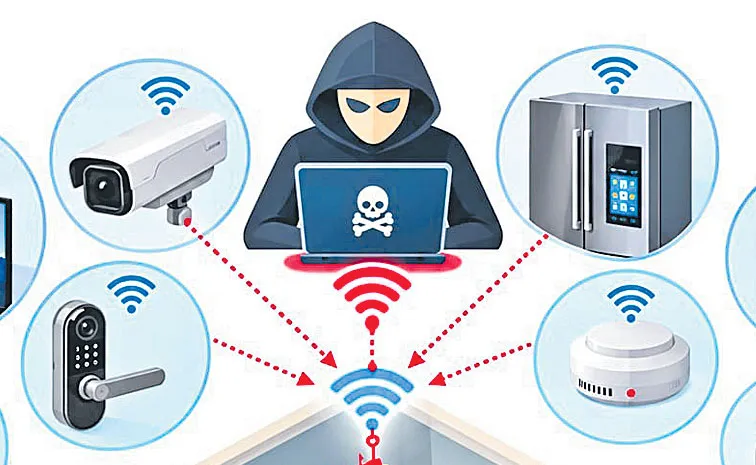
The agency identified exposed credentials in source code repositories, continuous integration and continuous delivery (CI/CD) variables, configuration files, client applications and cloud storage as possible pathways for unauthorised access. CERT-In also warned that cybercriminals are exploiting publicly available AI-based offensive security frameworks to target organisations in India and other countries. AI-assisted attacks can shorten the time between an initial breach and damaging activity, with some operations reportedly completed within hours rather than days. CERT-In urged organisations to restrict AI agents’ permissions, secure credentials, review cloud access controls, remove exposed secrets and monitor systems for suspicious activity. The advisory highlights the growing need for stronger cybersecurity safeguards as AI tools become more capable.
Comments (0)
No comments yet
Be the first to comment!