Gossips
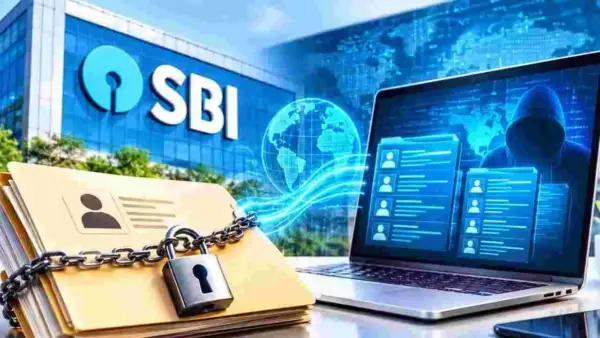
State Bank of India (SBI), the country's largest public-sector bank, has reported receiving alerts about a data leak involving 3,897 customers. According to the report, cybercriminals posted personal and banking information belonging to these customers on the dark web. SBI said it received warnings about the incident on the 16th of the month from the Defence Cyber Agency (DCA) and the Indian Computer Emergency Response Team (CERT-In). The bank stated that its banking operations had not been disrupted and that it was assessing the potential impact of the leak. It also reassured customers that the reported exposure of information does not mean their account balances have been lost. However, the incident raises concerns about possible fraud attempts using leaked information. SBI has advised customers not to disclose their PINs, one-time passwords (OTPs), passwords or other confidential banking details to anyone claiming to be a bank employee over the phone.
Separately, a leak involving sensitive information from HDFC Bank has also been reported. The report states that two senior officials of the bank were identified as having leaked business strategies and other confidential information. In another cybersecurity development, experts reportedly discovered that eight digital certificates issued by Indian cybersecurity company e-Mudhra in the previous year had weak cryptographic keys that could be cracked in about one second. Such weaknesses could potentially allow attackers to create fraudulent websites and redirect users without browsers detecting the deception. Following the discovery, Google, Apple, Mozilla and Microsoft reportedly blocked e-Mudhra's digital certificates. These incidents highlight the importance of robust cybersecurity controls, secure digital certificates and prompt responses to data breaches. Customers should remain alert to suspicious calls and messages, use official banking channels and never share confidential credentials.
Comments (0)
No comments yet
Be the first to comment!