Movies
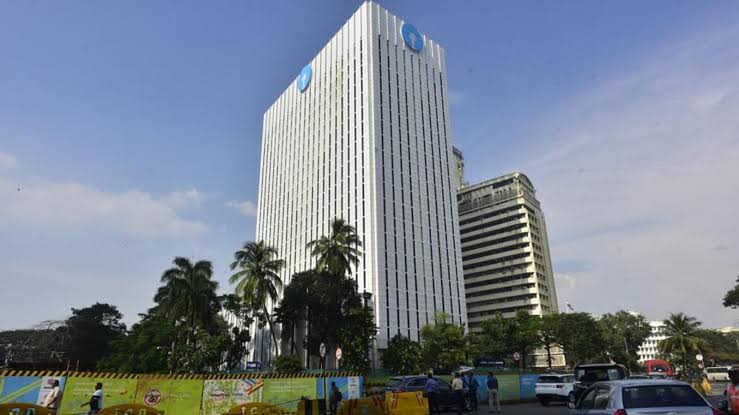
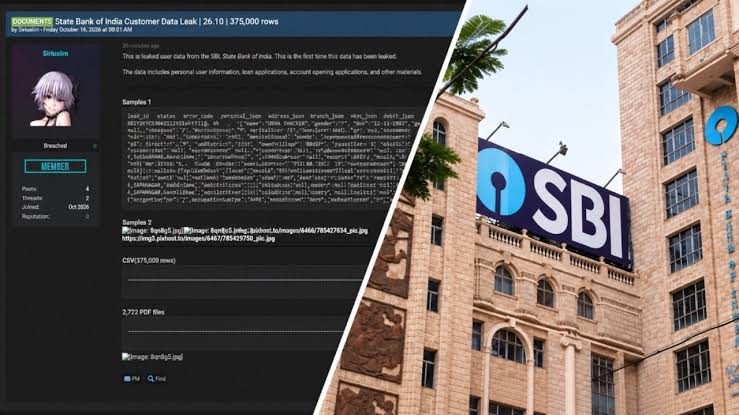
State Bank of India (SBI), the country’s largest public sector bank, has confirmed a cybersecurity incident involving the suspected exposure of customer information on the dark web. According to the bank’s disclosure, data belonging to 3,897 customers was reportedly exposed. In an exchange filing on Wednesday, SBI stated that it had reported an incident involving the loss of some data. The bank said a detailed investigation was necessary to determine the cause of the incident and assess its potential impact on both customers and the bank.
According to SBI, on October 16, 2026, it received information from CERT-In and its threat intelligence service provider regarding an alert about the suspected exposure of customer data on the dark web. The information reportedly included customers’ registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch details, Customer Information File (CIF) identifiers, lead IDs, loan and lead records, and metadata associated with other related files. The exposure of such information could create risks of targeted scams and misuse of personal data. However, the full circumstances and extent of the incident are still being investigated.
To examine the incident, SBI has appointed an independent cybersecurity agency empanelled with CERT-In to conduct a comprehensive investigation. The bank has assured customers that the incident is not expected to affect its core business operations or financial performance. It has also stated that its regular banking activities are continuing without disruption. The investigation is expected to establish how the data was exposed, the potential consequences for affected customers and whether additional protective measures are required.
Comments (0)
No comments yet
Be the first to comment!