Sports
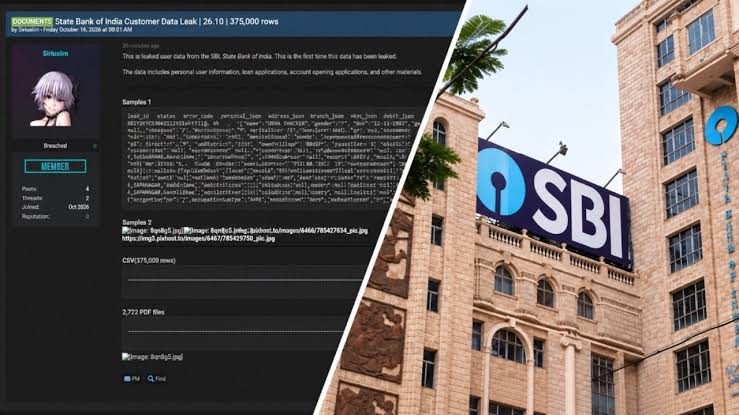
A claim about a possible data leak involving State Bank of India (SBI), the country’s largest public sector bank, has sparked discussions on social media. An unidentified hacking group reportedly operating under the name “Siriusim” has allegedly claimed to possess information related to SBI customers, including personal details, loan applications and documents submitted when opening bank accounts. According to a post shared on X by CyberPulse56, a cybersecurity-focused social media account, the group allegedly possesses around 3.8 lakh data records and 2,722 PDF documents. However, these claims have not yet been independently verified.
If the leaked information is genuine, it could potentially expose customers to cybercrime and financial fraud. Criminals may use such information to impersonate bank officials, make fraudulent phone calls, send fake messages or trick customers into revealing confidential details. Information such as residential addresses and loan application records could also be misused for targeted scams. However, the allegations alone do not establish that SBI’s servers were hacked or that the bank’s systems were compromised. The source of the alleged data, its authenticity and the number of customers potentially affected remain unclear.
The incident has once again highlighted the importance of cybersecurity in the banking sector, where mobile banking, online transactions and digital loan applications are increasingly common. Customers are advised not to share their OTPs, ATM PINs or passwords with anyone claiming to be a bank official. They should avoid clicking on suspicious links, regularly check their account transactions and immediately contact their bank if they notice any unauthorised activity. Until official confirmation is available, customers should treat the data leak claim as unverified while remaining vigilant against possible scams.
Comments (0)
No comments yet
Be the first to comment!